Choosing a Payment Gateway for Your App
First, successful payment integration starts with choosing a proper gateway. Moreover, it must match your target markets and payment methods. Therefore, you should consider supported currencies, cards, digital wallets, fees, and integration requirements before making a final decision.
- Market Support: Make sure the gateway supports the currencies and payment methods required by your target users.
- Payment Variety: Choose a solution that supports cards, wallets, and relevant digital payment options.
- Easy Integration: Well-documented APIs and SDKs can reduce development time and simplify future maintenance.
Designing the Payment Integration
First, your payment logic must be separated from the rest of the app. This creates a reliable transaction flow. Consequently, it becomes much easier to manage orders, verify transactions, and add new payment methods later.
- Create Secure Orders: Generate a unique identifier for every transaction and connect it to the related order.
- Verify Transaction Results: Do not rely only on the interface response; verify the transaction status through a trusted source.
- Update Order Status: Connect successful and failed payments to clear order states to prevent incorrect order processing.
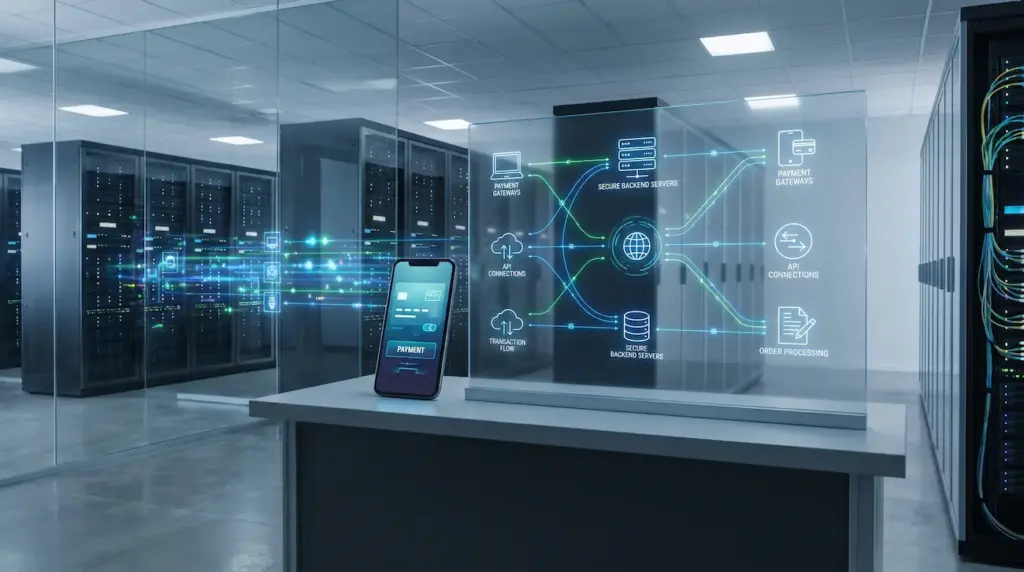
Protecting Payment Data in Transit
Financial data always requires strong protection during transmission. As a result, secure communication and limited data exposure will significantly reduce security risks.
- Encrypt Communications: Use secure communication protocols to protect financial information during transmission.
- Minimize Sensitive Data: Avoid storing sensitive card information when it is not operationally necessary.
- Secure Access Keys: Store secret keys and credentials in protected environments instead of placing them directly inside applications.
Applying PCI DSS Requirements
Payment compliance depends on how data is handled and protected. Furthermore, PCI DSS provides essential security requirements designed to protect payment account data and reduce risks.
- Define Data Scope: Identify where payment information moves and which systems can affect its security.
- Control Access: Provide only the permissions required for each role and monitor access to sensitive systems.
- Test Security Controls: Perform regular security assessments to identify weaknesses before they become serious problems.
- PCI Standards: The PCI Security Standards Council explains that PCI DSS applies to organizations that store, process, or transmit payment account data.
Reducing Failed Payment Transactions
Payment failures often result from incorrect inputs or technical errors. Therefore, a well-designed system should handle each failure clearly while preventing duplicate charges.
- Classify Failure Reasons: Separate bank declines, technical errors, and session issues to determine the appropriate response.
- Support Safe Retries: Allow users to retry failed payments while using unique transaction identifiers to prevent duplication.
- Record Technical Errors: Maintain useful error logs without storing sensitive financial information.
Using Webhooks for Payment Verification
Webhooks allow your application to receive transaction status updates directly from the gateway. Moreover, they should be treated as an essential part of the payment lifecycle.
- Verify the Source: Validate signatures or authentication mechanisms provided by the payment gateway.
- Prevent Duplicate Events: Use transaction identifiers to ensure the same payment notification is not processed repeatedly.
- Handle Delayed Updates: Design the system to process notifications that arrive after the original payment attempt.
Improving the Payment Experience
Every unnecessary step can increase user abandonment rates. Therefore, a simple payment interface must clearly communicate whether a transaction succeeded, failed, or is processing. According to Worldpay’s 2024 report, digital payments accounted for about 66% of global e-commerce value.
- Reduce Steps: Request only the necessary information and keep the payment flow straightforward.
- Use Clear Messages: Explain payment failures and provide the next action instead of displaying technical errors.
- Support Different Devices: Test the payment experience across the major devices, operating systems, and browsers.
Supporting Digital Wallets and Payment Methods
Providing multiple options gives users more flexibility. Furthermore, a flexible architecture makes it easier to add new options as user expectations change. Worldpay reported that digital methods represented roughly 67% of global e-commerce value in 2025.
- Add Digital Wallets: Support relevant digital wallets to give users alternatives to traditional card payments.
- Support Multiple Methods: Build a flexible payment layer that can accommodate additional methods as the app grows.
- Standardize Results: Handle successful and failed transactions consistently regardless of the selected method.
Monitoring Payment Performance
Payment integration should be monitored after launch. Thus, continuous tracking helps reveal technical issues before they affect users. Worldpay noted that global digital payments increased from $1.7 trillion in 2014 to $18.7 trillion in 2024.
- Payment Success Rate: Compare successful transactions with total attempts to identify unusual performance changes.
- Failure Reasons: Monitor rejection and error categories to determine whether problems are technical or payment-related.
- Response Time: Measure transaction response times to detect delays that could negatively affect the customer experience.
Testing Before Payment Launch
Payment integration must be thoroughly tested before launch. Additionally, PCI DSS 4.x introduced updated requirements effective March 31, 2025, emphasizing stronger and continuously monitored security controls.
- Test Success and Failure: Simulate successful, rejected, interrupted, and delayed transactions to verify correct system behavior.
- Test Security: Review access controls, API credentials, data protection, and integration points before production deployment.
- Test Refunds: Confirm that cancellations and refunds are processed correctly and reflected in the related order status.